Attackers do not break in, they log in. Put your people inside the exact moment it happens, from a phishing email to a bank-detail switch, and let them make the call. Judgement becomes muscle memory. Free to play, no sign-up.
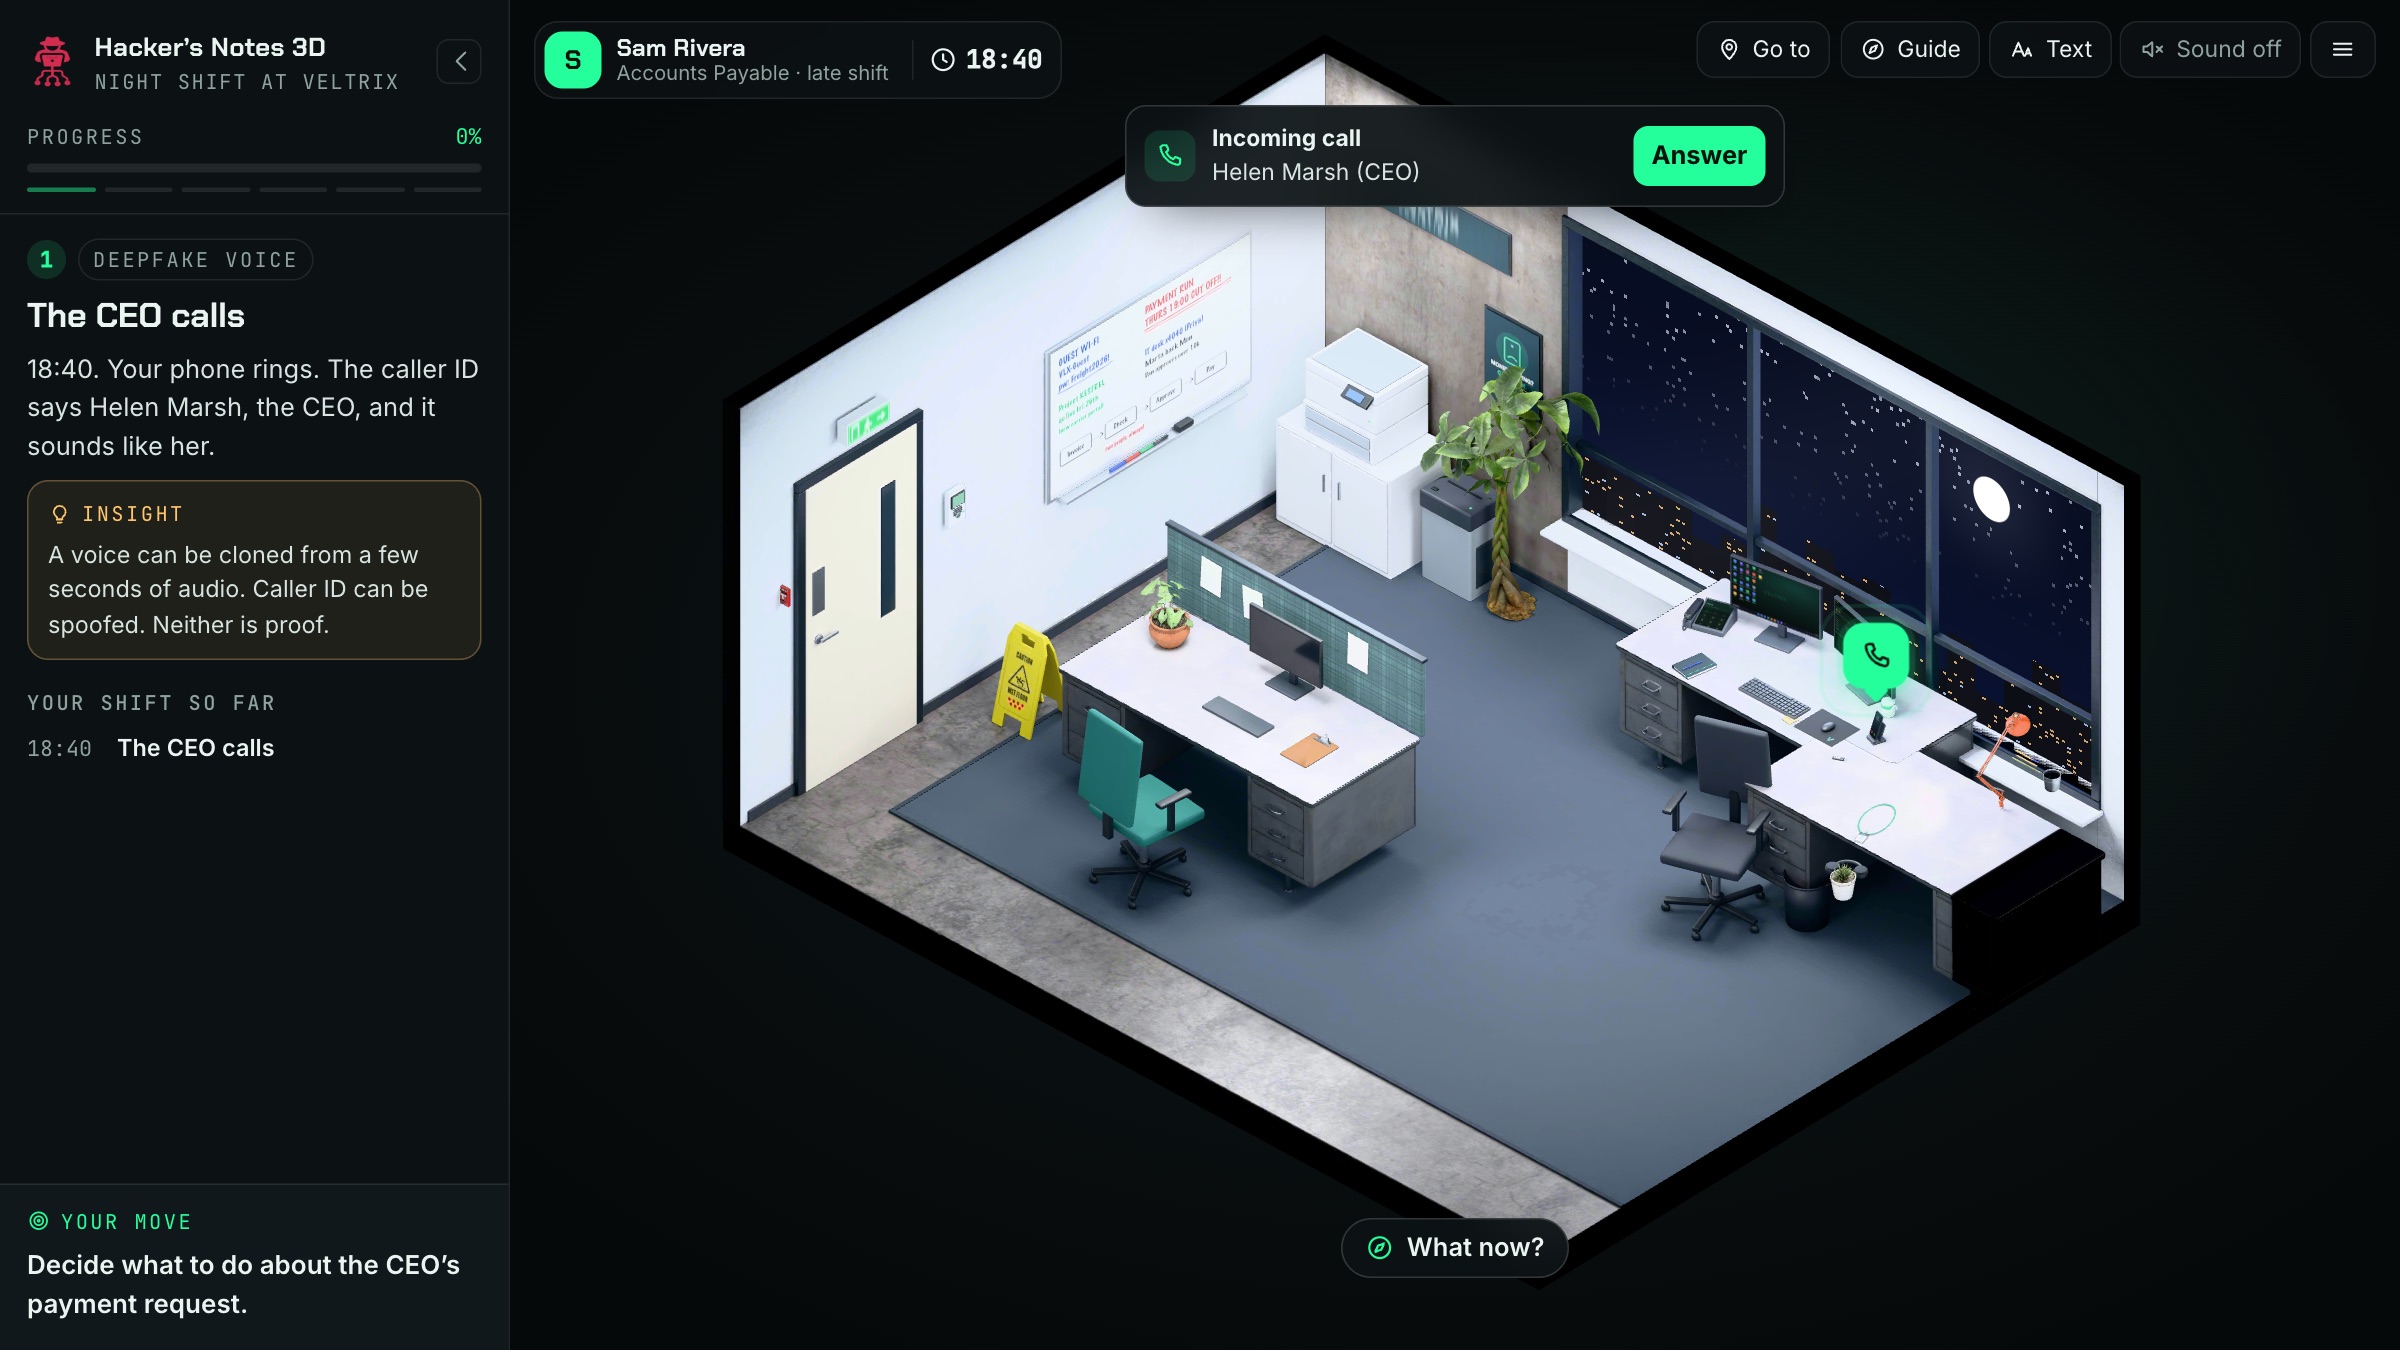
Every drill drops your people inside an interactive 3D scene and lets them handle the exact moment an attack lands. They investigate, they decide, and they watch it play out. That is what sticks.
A different shape of training: a decision under pressure, a real consequence, and a debrief that names the habit.
Each exercise is a real workday scene, rebuilt in 3D. The email, the call, the request to change a bank detail. Not a slide about it.
They act, under a little time pressure, the way they would at their desk. There is a right move and a wrong one, and the wrong one is allowed.
The scene plays out the consequence either way, then a short debrief names the habit that would have caught it. That is what sticks.
A core awareness track for everyone, and deeper tracks for the teams that build and run your software.
Phishing, ransomware, social engineering, and the everyday judgement calls that keep an attacker out.
GDPR, data handling, retention, and the EU AI Act, taught through the decisions people make with real data.
Prompt injection, data leakage, shadow AI, and giving an assistant only the reach it should have.
Playable case studies drawn from documented breaches, with the names changed and the lessons kept.
For developers: injection, cross-site scripting, SSRF, and the auth mistakes that ship most often.
Broken object-level authorization, mass assignment, rate limits, and keys that see too much.
Secrets in commits, malicious pull requests, branch protection, and dependency confusion.
Storage misconfigurations, IAM least privilege, exposed dashboards, and locking down the root account.
One new drill in your inbox a week. No sign-up on the site, just an email address.
Just your email. One drill a week. Unsubscribe anytime.
Need a custom drill pack? Get in touch.Mapped to what you report on
Every drill carries its framework mapping, so coverage lines up with the standard you answer to.
Send a link. It works on a laptop or a phone, on the office network or at home. Nothing to deploy, nothing to sign in to.
Every exercise carries its OWASP, NIST, ISO, GDPR, MITRE or CIS mapping, so coverage lines up with the standard you answer to.
A core awareness track for everyone, and deeper tracks for developers, platform and cloud teams. One catalogue, many audiences.
Every phishing page and fake login inside an exercise is inert. It is a rehearsal, on purpose, with fictional companies throughout.
Yes. Every drill marked Play runs free in your browser, no sign-up and no card.
No. It is a web page. Send a link and it works on a laptop or a phone, on the office network or at home.
No. Every phishing page and fake login inside a drill is inert and submits nothing. Nothing your people do in a drill leaves their device.
No. Every company, person, domain and message in a drill is fictional, on purpose. It is a rehearsal, not a trap.
Every drill carries its OWASP, NIST, ISO, GDPR, MITRE or CIS mapping, so you can show coverage against the standard you report on.
Yes. Send the link to as many people as you like. There is no seat count and no install, so a whole team or a whole company can play the same drill.